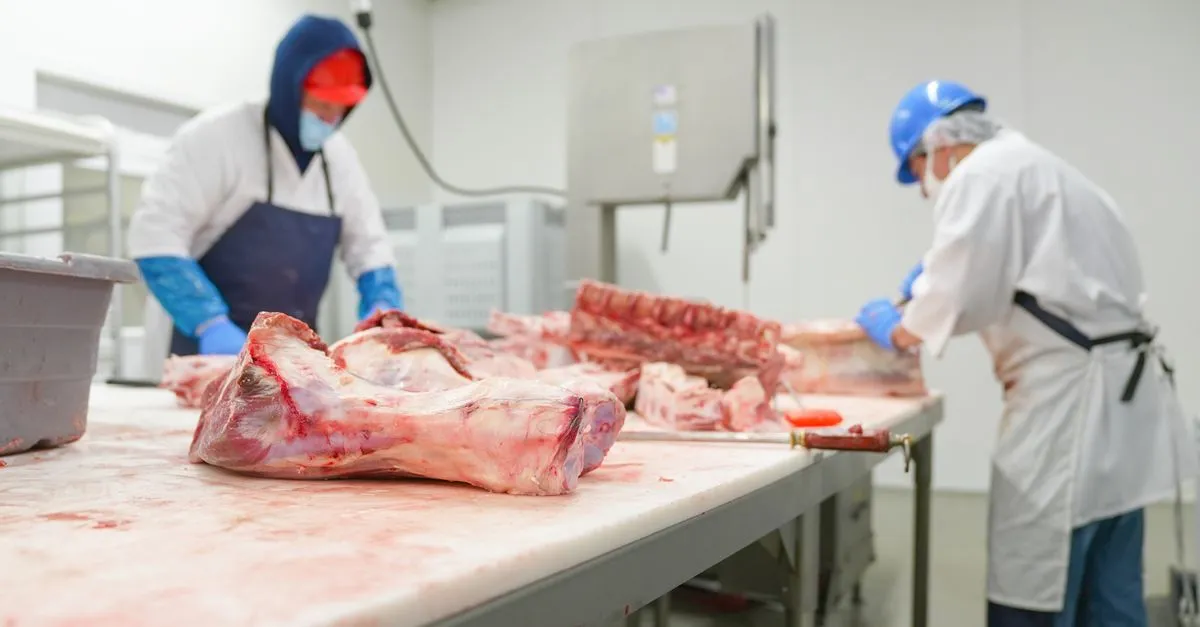
The National Cyber Security Centre (NCSC) has reported several cyber incidents within the European food sector. The centre currently sees no reason to assume that the incidents are connected.
As the national CSIRT and sectoral CSIRT for designated organisations, the NCSC monitors relevant developments and cyber threats affecting the Netherlands 24/7. It investigates facts, exchanges information with the parties and partners involved, and provides information, advice and guidance on what action to take. The NCSC does not make substantive statements about individual organisations or ongoing investigations.
The Cyber Security Act (Cbw) has been in force since 15 August and applies to approximately 8,000 organisations in eighteen (highly) critical sectors, including energy, digital infrastructure, research and government. Larger companies in other sectors and some suppliers may also fall under the Act.
In the event of significant cyber incidents, organisations must report them to their sector’s CSIRT and the relevant supervisory authority. According to the NCSC, these reports help to build a complete picture of the situation, provide support to affected organisations and prevent possible incidents at other organisations.